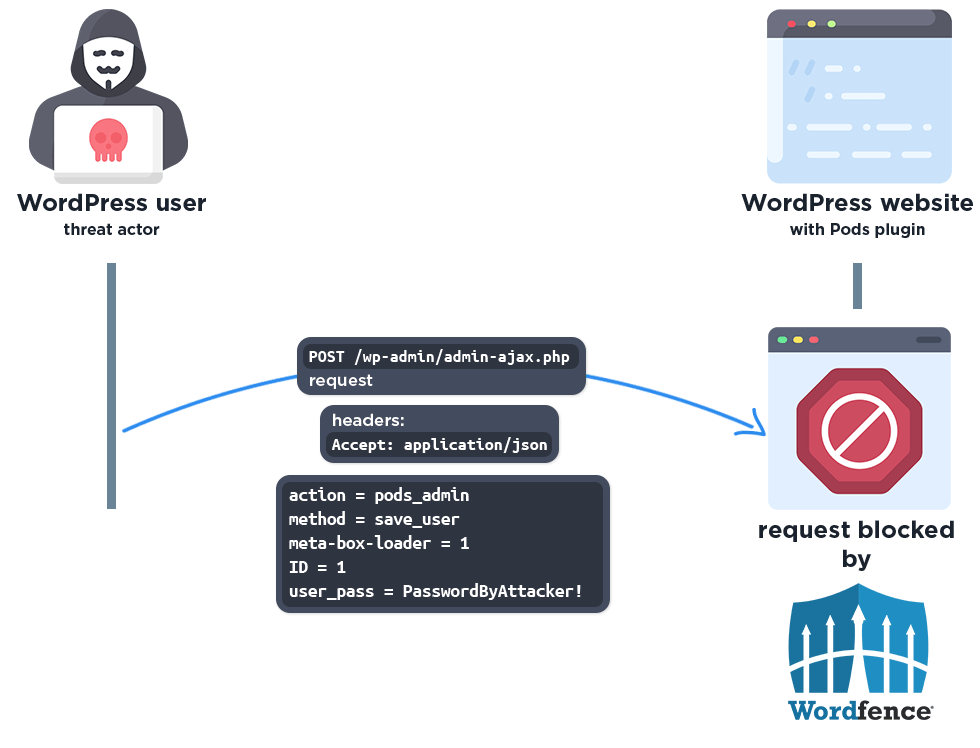
A critical security vulnerability discovered in the Pods WordPress plugin is putting more than 100,000 websites at risk of complete takeover. The flaw, an unauthenticated privilege escalation vulnerability, was submitted to Wordfence on August 10th, 2026, and allows attackers with no prior authentication to elevate their privileges to administrator level on any affected site.
According to Wordfence, which received the submission through its bug bounty program, the vulnerability is severe in scope. An attacker exploiting the flaw can overwrite the password of any user account on the site — including the site owner’s — effectively locking out legitimate users and seizing full control. Once administrative access is obtained, an attacker could modify content, install malicious plugins, exfiltrate data, or use the compromised site as a platform for further attacks.
Pods is a well-established plugin in the WordPress ecosystem, used to create and manage custom content types, fields, and relationships. Its broad adoption — reflected in its 100,000-plus active installations — makes the vulnerability particularly significant. Sites running the plugin in an unpatched state are potentially exposed to exploitation without requiring any credentials or social engineering on the attacker’s part, lowering the barrier for malicious actors considerably.
WordPress site administrators running the Pods plugin are strongly advised to check for available updates and apply patches immediately. Reviewing administrator accounts for any unauthorized changes and auditing recent site activity are also recommended precautionary steps. Wordfence users with the appropriate protection rules in place may have additional mitigation, but updating the plugin itself remains the primary remediation action.