Filtered by category: WordFence, tag: woocommerce × Clear
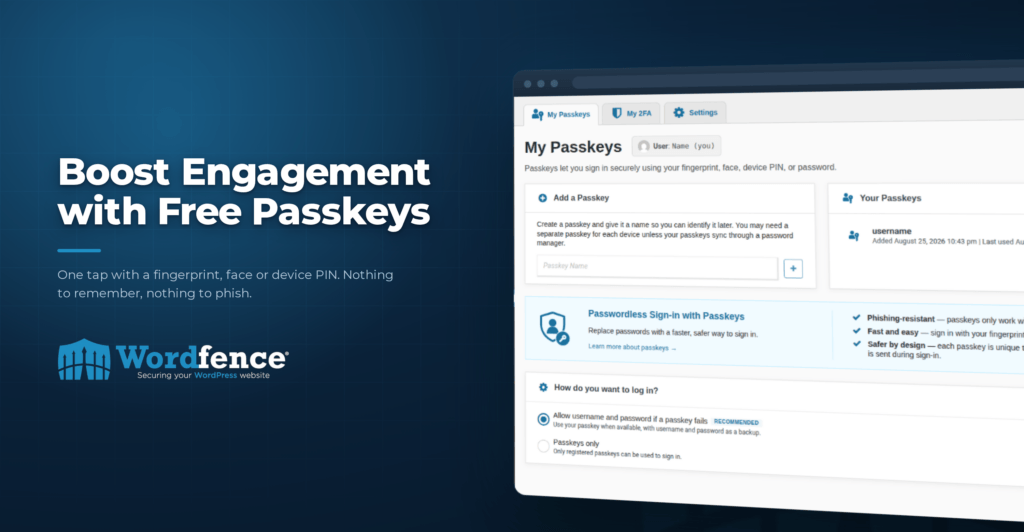
Boost Engagement with Free Passkeys by Wordfence
Matched: WordPress
Wordfence 9 introduces free passkeys for WordPress and WooCommerce sites, allowing users to sign in with a single click using fingerprint, facial recognition, or a PIN instead of a password. Available in both free and paid versions, passkeys reduce login friction and improve security by eliminating passwords that could be phished. Admins can make passkeys optional or required per user role, and users can register multiple passkeys across devices.
Attackers Actively Exploiting Critical Vulnerability in WooCommerce Wholesale Lead Capture Plugin
Matched: WordPress
A critical unauthenticated arbitrary file upload vulnerability (CVE-2026-27540, CVSS 9.8) in the WooCommerce Wholesale Lead Capture WordPress plugin allows attackers to upload PHP webshells and achieve remote code execution. The flaw exists because file type restrictions rely on attacker-controlled request data. With ~6,000 active installations, Wordfence has blocked over 100,000 exploit attempts. Users should update to version 2.0.3.2 immediately.