Filtered by tag: webshell × Clear
PHP Webshell Campaign Targets WordPress Through Critical WooCommerce Plugin Bug
Matched: WordPress
Attackers are exploiting a critical vulnerability in a third-party WooCommerce plugin to upload PHP webshells onto WordPress sites, gaining persistent backdoor access. The flaw allows unauthenticated file uploads, enabling remote code execution. Site owners are urged to update the affected plugin immediately and scan for indicators of compromise, including suspicious PHP files in upload directories.
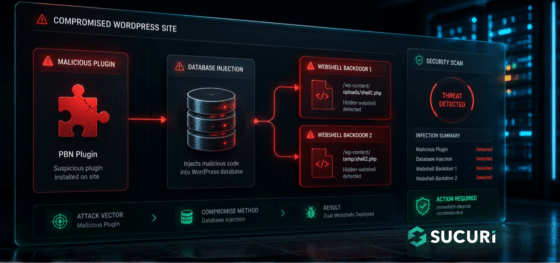
WordPress PBN Plugin Drops Dual Webshells via Database Injection
Matched: WordPress
A Turkish-speaking threat actor deployed a fake WordPress plugin that injects two PHP webshells directly into the database rather than the filesystem. The multi-stage attack uses a remote C2 server and hidden backlink injection to build a Private Blog Network for SEO monetization, likely serving gambling and adult affiliate schemes. Storing malware in the database helps evade traditional file-based security scans.