Filtered by tag: woocommerce × Clear
PHP Webshell Campaign Targets WordPress Through Critical WooCommerce Plugin Bug
Matched: WordPress
Attackers are exploiting a critical vulnerability in a third-party WooCommerce plugin to upload PHP webshells onto WordPress sites, gaining persistent backdoor access. The flaw allows unauthenticated file uploads, enabling remote code execution. Site owners are urged to update the affected plugin immediately and scan for indicators of compromise, including suspicious PHP files in upload directories.
Third-party WooCommerce plugin hits WordPress sites with PHP backdoor abusing recently patched vulnerability
Matched: WordPress
A critical unauthenticated file-upload vulnerability (CVE-2026-27540) in the WooCommerce Wholesale Lead Capture Plugin is being actively exploited to deploy PHP webshells capable of full site takeover. Affecting versions 2.0.3.1 and older, the flaw was patched in February 2026, but Wordfence has blocked over 100,000 attacks across two surge periods. The plugin has around 20,000 active installations. Users should update to v2.0.3.2 immediately and check upload directories for suspicious PHP files.

Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells
Matched: WordPress
Attackers are exploiting a critical flaw in the WooCommerce Wholesale Lead Capture WordPress plugin, which has over 6,000 active installs. The vulnerability allows unauthenticated attackers to upload arbitrary files, including PHP backdoors, enabling remote code execution. Wordfence has blocked multiple attack attempts targeting the flaw.
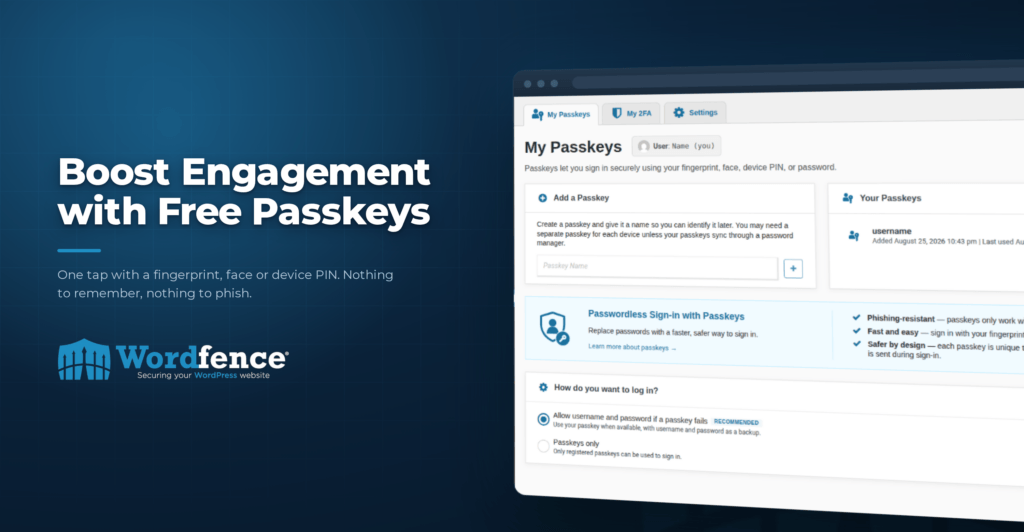
Boost Engagement with Free Passkeys by Wordfence
Matched: WordPress
Wordfence 9 introduces free passkeys for WordPress and WooCommerce sites, allowing users to sign in with a single click using fingerprint, facial recognition, or a PIN instead of a password. Available in both free and paid versions, passkeys reduce login friction and improve security by eliminating passwords that could be phished. Admins can make passkeys optional or required per user role, and users can register multiple passkeys across devices.
Attackers Actively Exploiting Critical Vulnerability in WooCommerce Wholesale Lead Capture Plugin
Matched: WordPress
A critical unauthenticated arbitrary file upload vulnerability (CVE-2026-27540, CVSS 9.8) in the WooCommerce Wholesale Lead Capture WordPress plugin allows attackers to upload PHP webshells and achieve remote code execution. The flaw exists because file type restrictions rely on attacker-controlled request data. With ~6,000 active installations, Wordfence has blocked over 100,000 exploit attempts. Users should update to version 2.0.3.2 immediately.